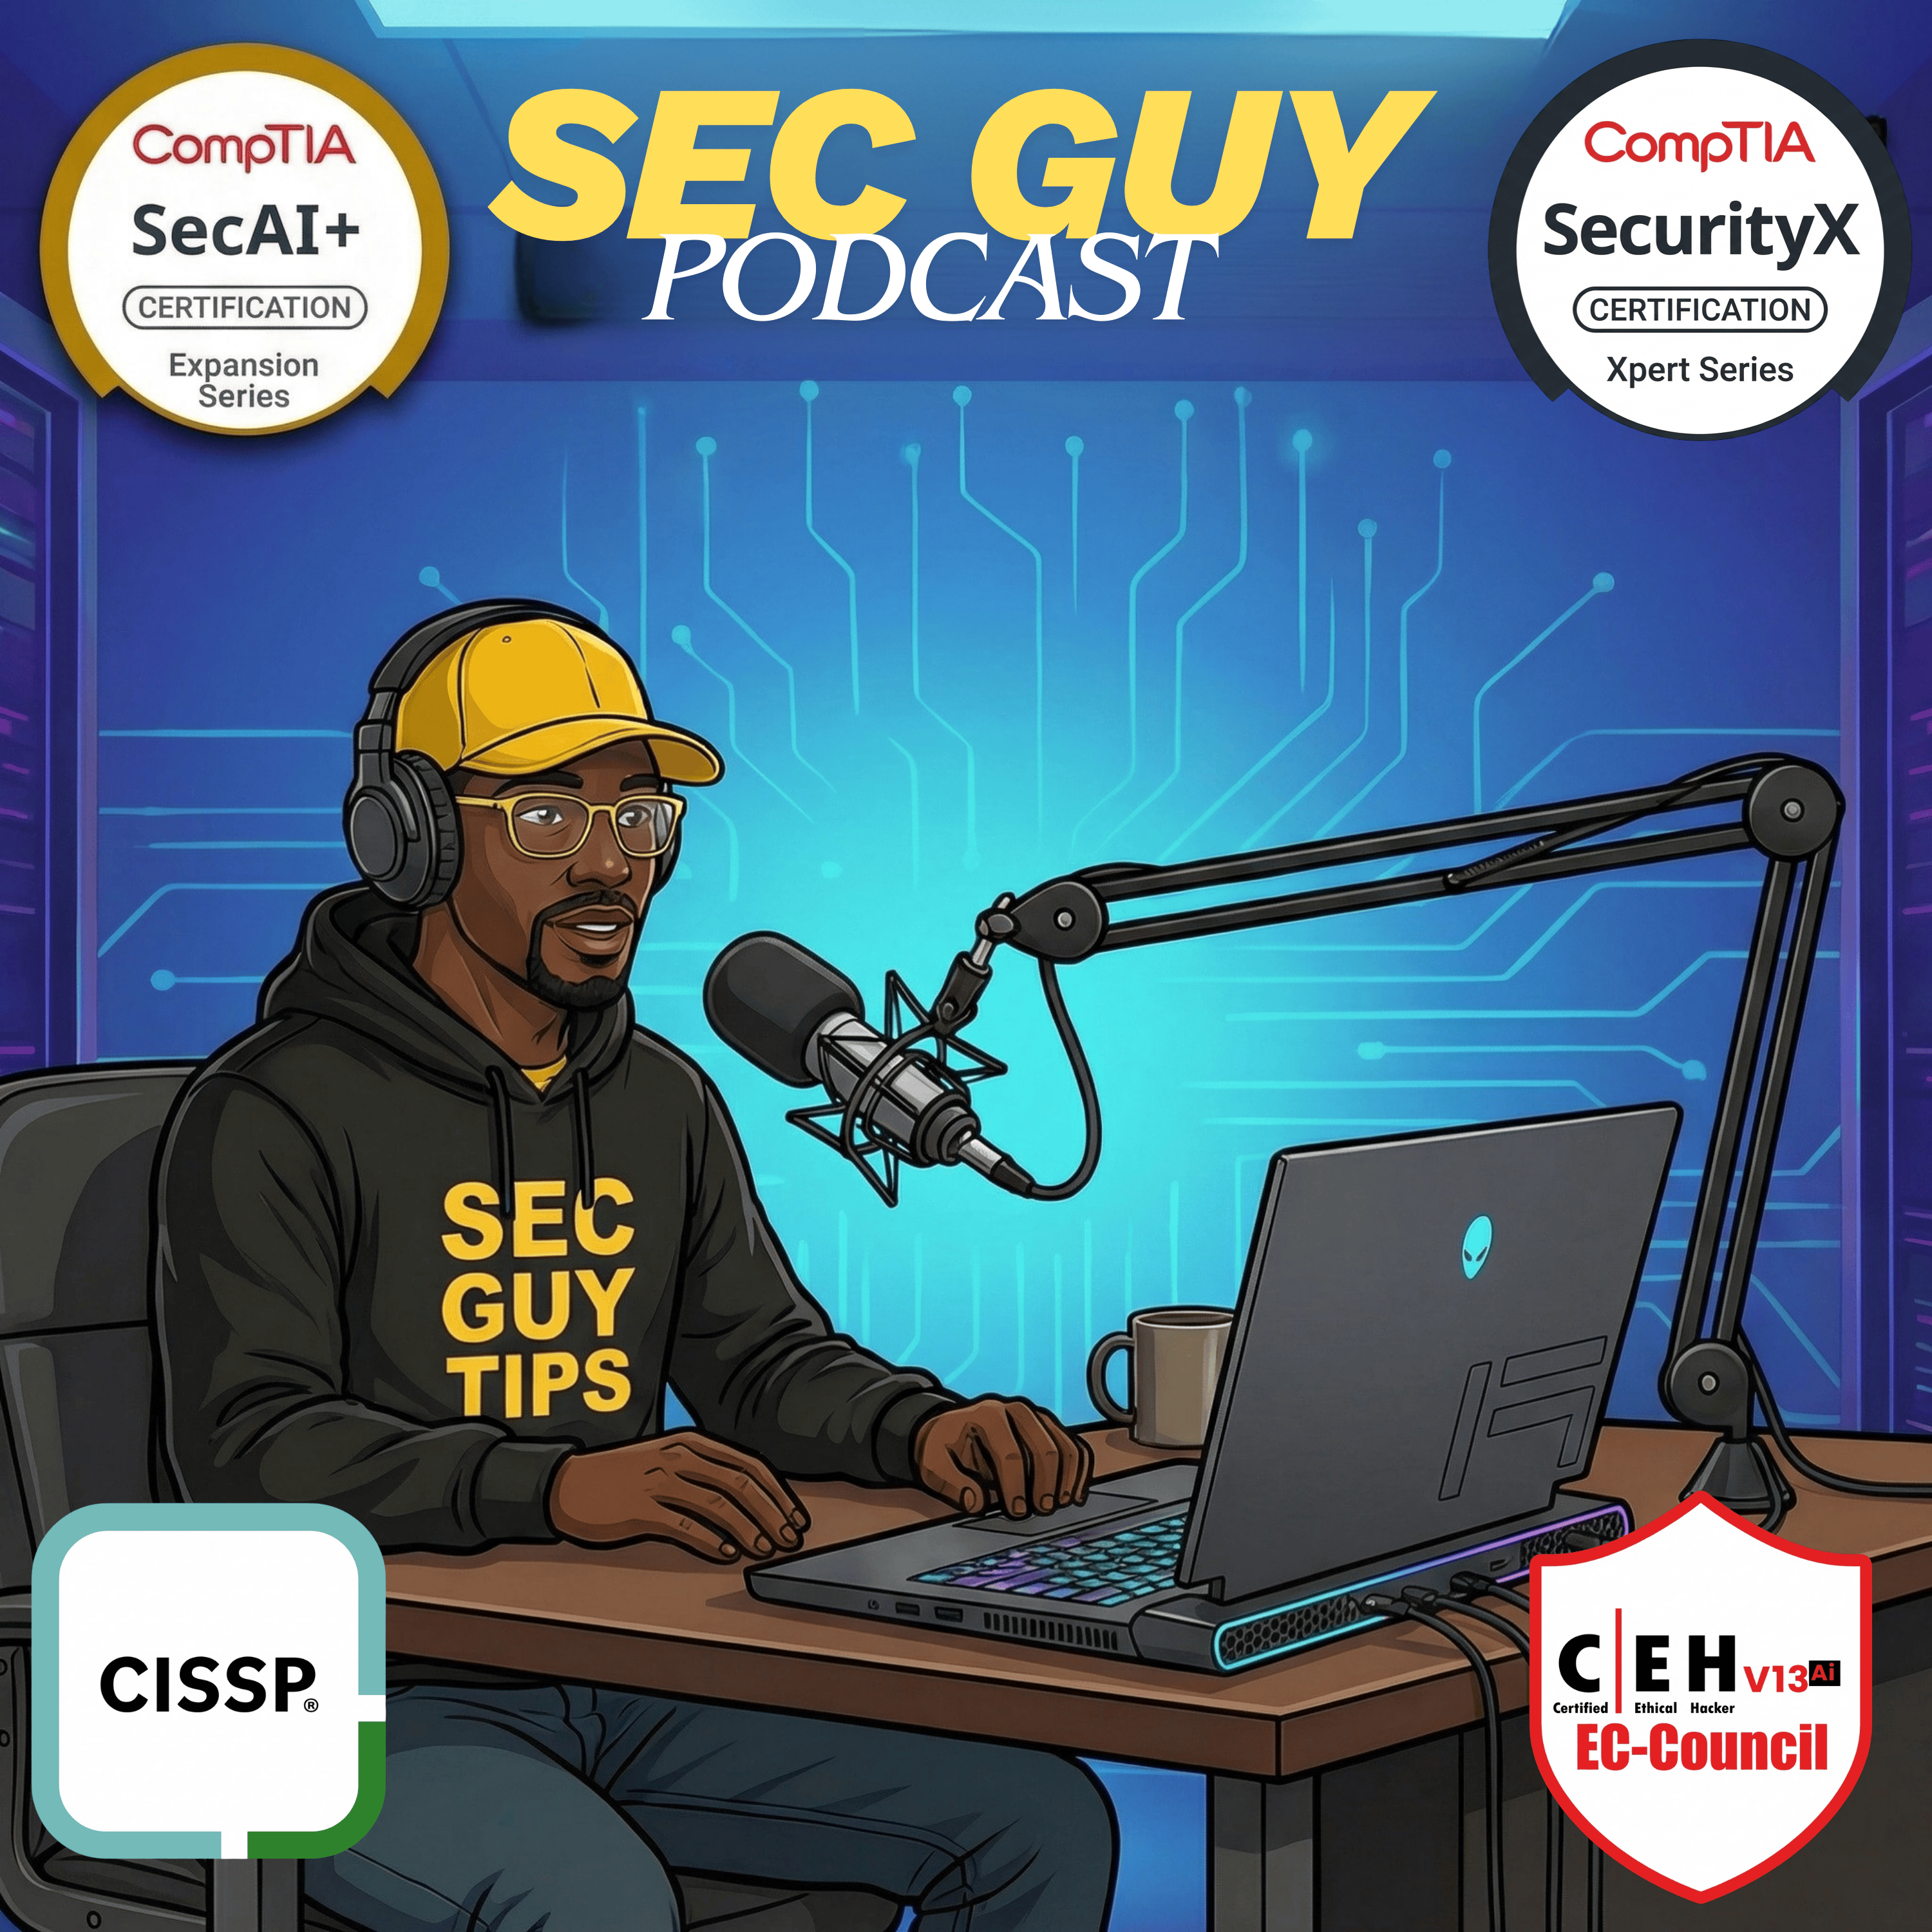
Sec Guy
Sec Guy
Real cybersecurity training for the real world. We take the complex theories of CompTIA Security+ and SecAI+ and translate them into actionable skills. Whether you're fighting off Prompt Injection attacks or just fighting to get your first IT job, the Sec Guy has your back. Join us for deep dives into AI Security, Network Defense, and the future of cyber. Train Hard. Stay Secure.
Be sure to visit the podcast's website and support the creator: rss.com
Where to listen?
Podcasts in the app Replaio Radio Coming soonPodcasts are coming to the app soon. Install now and be the first to see a whole new take on podcasts
 Install for free
Android almost 10M downloads · 4.8 rating
iOS soon
Episodes
Incident Response: Forensics, Diamond Model, IOC, IOA 17.09.2026 5:54
You don't build an Incident Response plan during a breach. In this video, Sec Guy dissects the massive Salt Typhoon attack to show you how professional responders hunt advanced threats. We break down the Diamond Model of Intrusion Analysis, explain why Indicators of Attack (IOA) are more valuable than Indicators of Compromise (IOC), and walk through the Order of Volatility for capturing forensic e...
Cryptography: PKI & Certificates: CA, OSCP, CRL, TLS 17.09.2026 5:06
Encryption protects your data, but PKI protects your trust. If you don't understand how a Certificate Authority (CA) validates a server, or why OCSP Stapling is faster than a CRL, you don't understand how the internet works. In this video, Sec Guy breaks down the "Trust Anchor" model, explains the difference between the Root CA and Intermediate CA, and walks you through the modern TLS 1.3 Handshak...
Identity Access Management: PAM, JIT, JEA, ABAC, SAML, OAuth 17.09.2026 5:56
In a cloud-native world, firewalls don't matter if your identity is compromised. "Identity is the New Perimeter." In this video, Sec Guy explains why Permanent Admin Rights are a security failure, how to implement Just-in-Time (JIT) access to stop attackers, and clearly defines the difference between SAML (XML/Enterprise), OAuth (Authorization), and OIDC (Authentication). 🔥🔥New Security+ SYO-801...
Risk Management: BCP, DRP, RTO/RPO & Risk Math 17.09.2026 8:32
In cybersecurity, we don't plan for if—we plan for when. In this video, Sec Guy explains why the old "3-2-1 Backup Rule" is no longer enough to stop ransomware, how to calculate the cost of a disaster using SLE, ARO, and ALE, and the critical difference between a Business Continuity Plan (BCP) and a Disaster Recovery Plan (DRP). 🔥🔥New Security+ SYO-801 Study Guide Available today: secguy.org/sec...
Modern Network Security: From Firewalls to Agentic AI Defense 17.09.2026 7:37
A firewall is no longer just a box—it's a policy enforcement engine. In this deep dive, Sec Guy explains why WAFs have evolved into WAAPs to stop API attacks, why VPNs are being replaced by ZTNA and SASE, and how to use "Sticky MAC" and 802.1X to lock down your physical ports. If you are prepping for Security+, CISSP, or CCSP, this is your masterclass in network defense. 🔥🔥New Security+ SYO-801...
Network Architecture: OSI Model, TCP/IP Model, PEP/PDP VLANS Explained 17.09.2026 5:52
If you can't map an attack to its layer, you can't defend against it. Is a DDoS attack Layer 4 or Layer 7? Is ARP Poisoning Layer 2 or Layer 3? In this video, Sec Guy breaks down the OSI Model vs. TCP/IP, explains the critical difference between the Policy Decision Point (PDP) and Policy Enforcement Point (PEP) in Zero Trust, and shows you how to stop VLAN Hopping attacks. 🔥🔥New Security+ SYO-80...
Infrastructure Attack Surfaces: Spectre, VM Escape, & Memory Mastery 17.09.2026 7:04
Software updates are great, but you can't patch a physics problem. In this video, Sec Guy explores the Infrastructure Attack Surface, explaining why Spectre and Meltdown exploit the CPU itself, how VM Escape can bring down an entire cloud provider, and the critical difference between a Buffer Overflow (Execution Attack) and a Memory Leak (Availability Attack). 🔥🔥New Security+ SYO-801 Study Guide...
Threat Vectors & Attack Surfaces Explained 17.09.2026 5:58
A "Threat Vector" is the path; an "Attack Surface" is the target. If you can't distinguish between a message-based attack (Smishing) and a file-based attack (Malicious Macro), you will lose points on your exam and miss threats in your SOC. In this video, Sec Guy maps out the 7 critical threat vectors you need to know, from Supply Chain compromises to Voice-based social engineering. 🔥🔥New Securit...
Security+ Domain 1: Question Walkthrough 17.09.2026 7:58
Join Sec Guy for an in-depth review of Domain 1 for the CompTIA Security+ (SY0-701) exam. This 10-question practice test covers everything from security principles and controls to governance and threat actors. Perfect for on-the-go studying! 🔥🔥New Security+ SYO-801 Study Guide Available today: secguy.org/security-study-guide 🔥🔥 0:00: Introduction to Domain 1: General Security Concepts. 0:06: O...
Threat Actors & Motivations 17.09.2026 4:46
If you don't know who is attacking you, you are just chasing ghosts. In this video, Sec Guy maps the adversary landscape—from highly funded Nation States (APTs) like Salt Typhoon to financially motivated Organized Crime groups like Scattered Spider. We also reveal why the "Insider Threat" and "Shadow IT" might be more dangerous to your organization than any elite foreign hacker. 🔥🔥New Security+...
Digital Signatures Explained: Non-repudiation, Hashing, Private Keys 17.09.2026 3:10
A digital signature is NOT just an image of your name on a PDF. It is a mathematical proof that guarantees three things: Authentication, Integrity, and Non-Repudiation. In this video, Sec Guy explains the exact workflow of signing a document (Hash - Encrypt with Private Key) and why this process makes it legally impossible for a sender to say "It wasn't me." 🔥🔥New Security+ SYO-801 Study Guide A...
Why Blockchain is Replacing Your Social Security Number 17.09.2026 3:10
Your Social Security Number is a password you can never change—and that is a security nightmare. In this video, Sec Guy explains why the future of identity isn't a static number in a database, but a cryptographic key in your wallet. We break down how Blockchain creates an immutable "Distributed Ledger" and how Self-Sovereign Identity (SSI) eliminates the single point of failure that hackers love....
Zero Trust Architecture Explained (CompTIA Security+, CISSP, CEH, SecAI+, GIAC) 17.09.2026 11:40
"Trust but Verify" is a failed strategy. In today's cloud-native world, the only safe assumption is "Never Trust, Always Verify." In this deep dive, Sec Guy unpacks the NIST 800-207 Zero Trust Architecture, explains the critical difference between the Policy Decision Point (PDP) and Policy Enforcement Point (PEP), and shows you how to stop lateral movement dead in its tracks. 🔥🔥New Security+ SYO...
Mastering Access Control: RBAC, MAC, DAC & The AAA Framework 17.09.2026 10:13
If you can't prove who you are, what you're allowed to do, and track what you did—you have no security. In this video, Sec Guy breaks down the AAA Framework (Authentication, Authorization, Accounting) and explains the critical differences between RBAC, MAC, and DAC that you must know for your exam and your career. [Exam Ready Route - FREE] Pass your certification for $0. ✅ Training Videos & P...
Mastering Security Controls: Preventive, Detective, & Corrective 17.09.2026 5:49
Firewalls aren't enough. To build a true defense-in-depth strategy, you need to understand the three pillars of security controls: Preventive, Detective, and Corrective. In this video, Sec Guy breaks down how these controls work together to secure your network, using real-world analogies to make the concepts stick for your exam and your career. [Exam Ready Route - FREE] Pass your certification for...
Security through Obscurity? Steganography & Obfuscation Explained 17.09.2026 3:48
"Security through Obscurity" is a delay tactic, not a defense strategy. In this video, Sec Guy explains why Obfuscation is different from Encryption, how hackers use Steganography to hide malware inside innocent JPEGs, and why Tokenization is the secret weapon for passing your PCI-DSS audits. 🔥🔥New Security+ SYO-801 Study Guide Available today: secguy.org/security-study-guide 🔥🔥 [Exam Ready Ro...
Encryption Explained: Symmetric vs. Asymmetric 17.09.2026 5:36
If you can't explain the difference between a "Private Key" and a "Public Key," you will fail your exam. In this video, Sec Guy breaks down the two main families of encryption, explains why we use Symmetric for speed (AES) and Asymmetric for security (RSA/ECC), and gives you the "23 BRAIDS" mnemonic to memorize every algorithm instantly. 🔥🔥New Security+ SYO-801 Study Guide Available today: secgu...
Hashing Explained - Digital Fingerprints & Data Integrity 17.09.2026 4:09
Hashing is NOT encryption—it's a one-way "meat grinder." In this video, Sec Guy explains the "Avalanche Effect," why MD5 and SHA-1 are dead, and how hackers use Rainbow Tables to crack unsalted passwords in milliseconds. If you don't understand the difference between a collision and a salt, you are not ready for your exam. 🔥🔥New Security+ SYO-801 Study Guide Available today: secguy.org/security-...
Physical Security in the AI Era 17.09.2026 7:25
We spend millions on firewalls, but if an insider can walk out the front door with your AI models in a backpack, your security program has failed. In this video, Sec Guy breaks down the Google AI theft case, explains why "Degaussing" destroys hard drives but fails on SSDs, and covers the critical exam concepts of CPTED, Man Traps, and Faraday Cages. 🔥🔥New Security+ SYO-801 Study Guide Available...
What is the CIA Triad? The Foundation of Cyber Security 17.09.2026 4:37
Confidentiality, Integrity, and Availability aren't just buzzwords—they are the backbone of every security strategy you will ever build. In this video, Sec Guy breaks down the "CIA Triad" with real-world examples (like hospital outages and bank hacks) to show you exactly how these three principles keep systems secure and why they are the first thing tested on your exam. [Exam Ready Route - FREE] P...
CompTIA Security+ Full Course 2026 17.09.2026 5:35
Welcome to the Sec Guy Channel and the start of your journey to becoming a cybersecurity professional! 🛡️ This is the first video in our comprehensive training series designed to help you pass the new CompTIA Security+ (SY0-701) exam. In this foundational video, "Exam Overview," we're breaking down everything you need to know before you start studying the core content. Understanding the exam logis...
SecAI+ Domain 4.2: Compliance & Law 02.02.2026 4:12
The Final Objective: Mastering the Law and Frameworks for global AI compliance. In the finale of our SecAI+ course, we cover Objective 4.3: Compliance and Frameworks. We break down the EU AI Act's risk-based approach, the four core functions of the NIST AI RMF, and the critical ISO standards (42001, 23894, 22989) you need for the exam. Plus, learn about Data Sovereignty and how the OECD Principles...
SecAi+ Domain 4.1: AI CoE, Responsible AI, and AI RIsk 02.02.2026 3:51
From the server room to the boardroom: Mastering AI GRC for the SecAI+ Exam. This episode covers Domain 4: AI Governance, Risk, and Compliance. We explore the AI Center of Excellence (CoE), identify the Builders, Defenders, and Watchers on an AI team, and deep-dive into the dangers of Shadow AI. Learn the essential Responsible AI Principles—Fairness, Transparency, and Accountability—needed to pass...
SecAI+ Domain 3.3: The AI Analyst (Blue Team Tools, MCP & Co-Pilot) 02.02.2026 3:44
We have seen the weapons (Video 10). Now, let’s look at the shields. Welcome to Domain 3: AI-Assisted Security. In this video (Objective 3.3), we switch to the Blue Team. We are breaking down the "AI Co-Pilot" stack, the new hardware you need to know for the exam, and the critical standard that connects AI to your internal data without causing a leak. In this video, we cover: The AI Co-Pilot: IDE...
SecAI+ Domain 3.1: The AI Analyst (Blue Team Tools, MCP & Co-Pilot) 02.02.2026 4:24
🛡️ Domain 3: AI-Assisted Security (Objective 3.1) We’ve analyzed the weapons in Domain 2—now it’s time to deploy the shields. Welcome to the Blue Team. In this video, we break down the "AI Co-Pilot" stack and the defensive tools you need to master for the SecAI+ exam. From the hardware powering Edge AI to the critical protocols that secure internal data, this is your crash course in AI-assisted...
Similar podcasts




Listen to the Sec Guy podcast in Replaio
Radio and podcasts in one app - free, with no sign-up. Install today and do not miss the launch
Replaio is not a podcast publisher; show names, artwork and audio belong to their authors and are distributed through public RSS feeds.